The problem
Cryptographic implementations can leak secrets through response timing even when their algorithms remain mathematically secure. These attacks and their mitigations are difficult to understand from formulas or static reports alone.
The approach
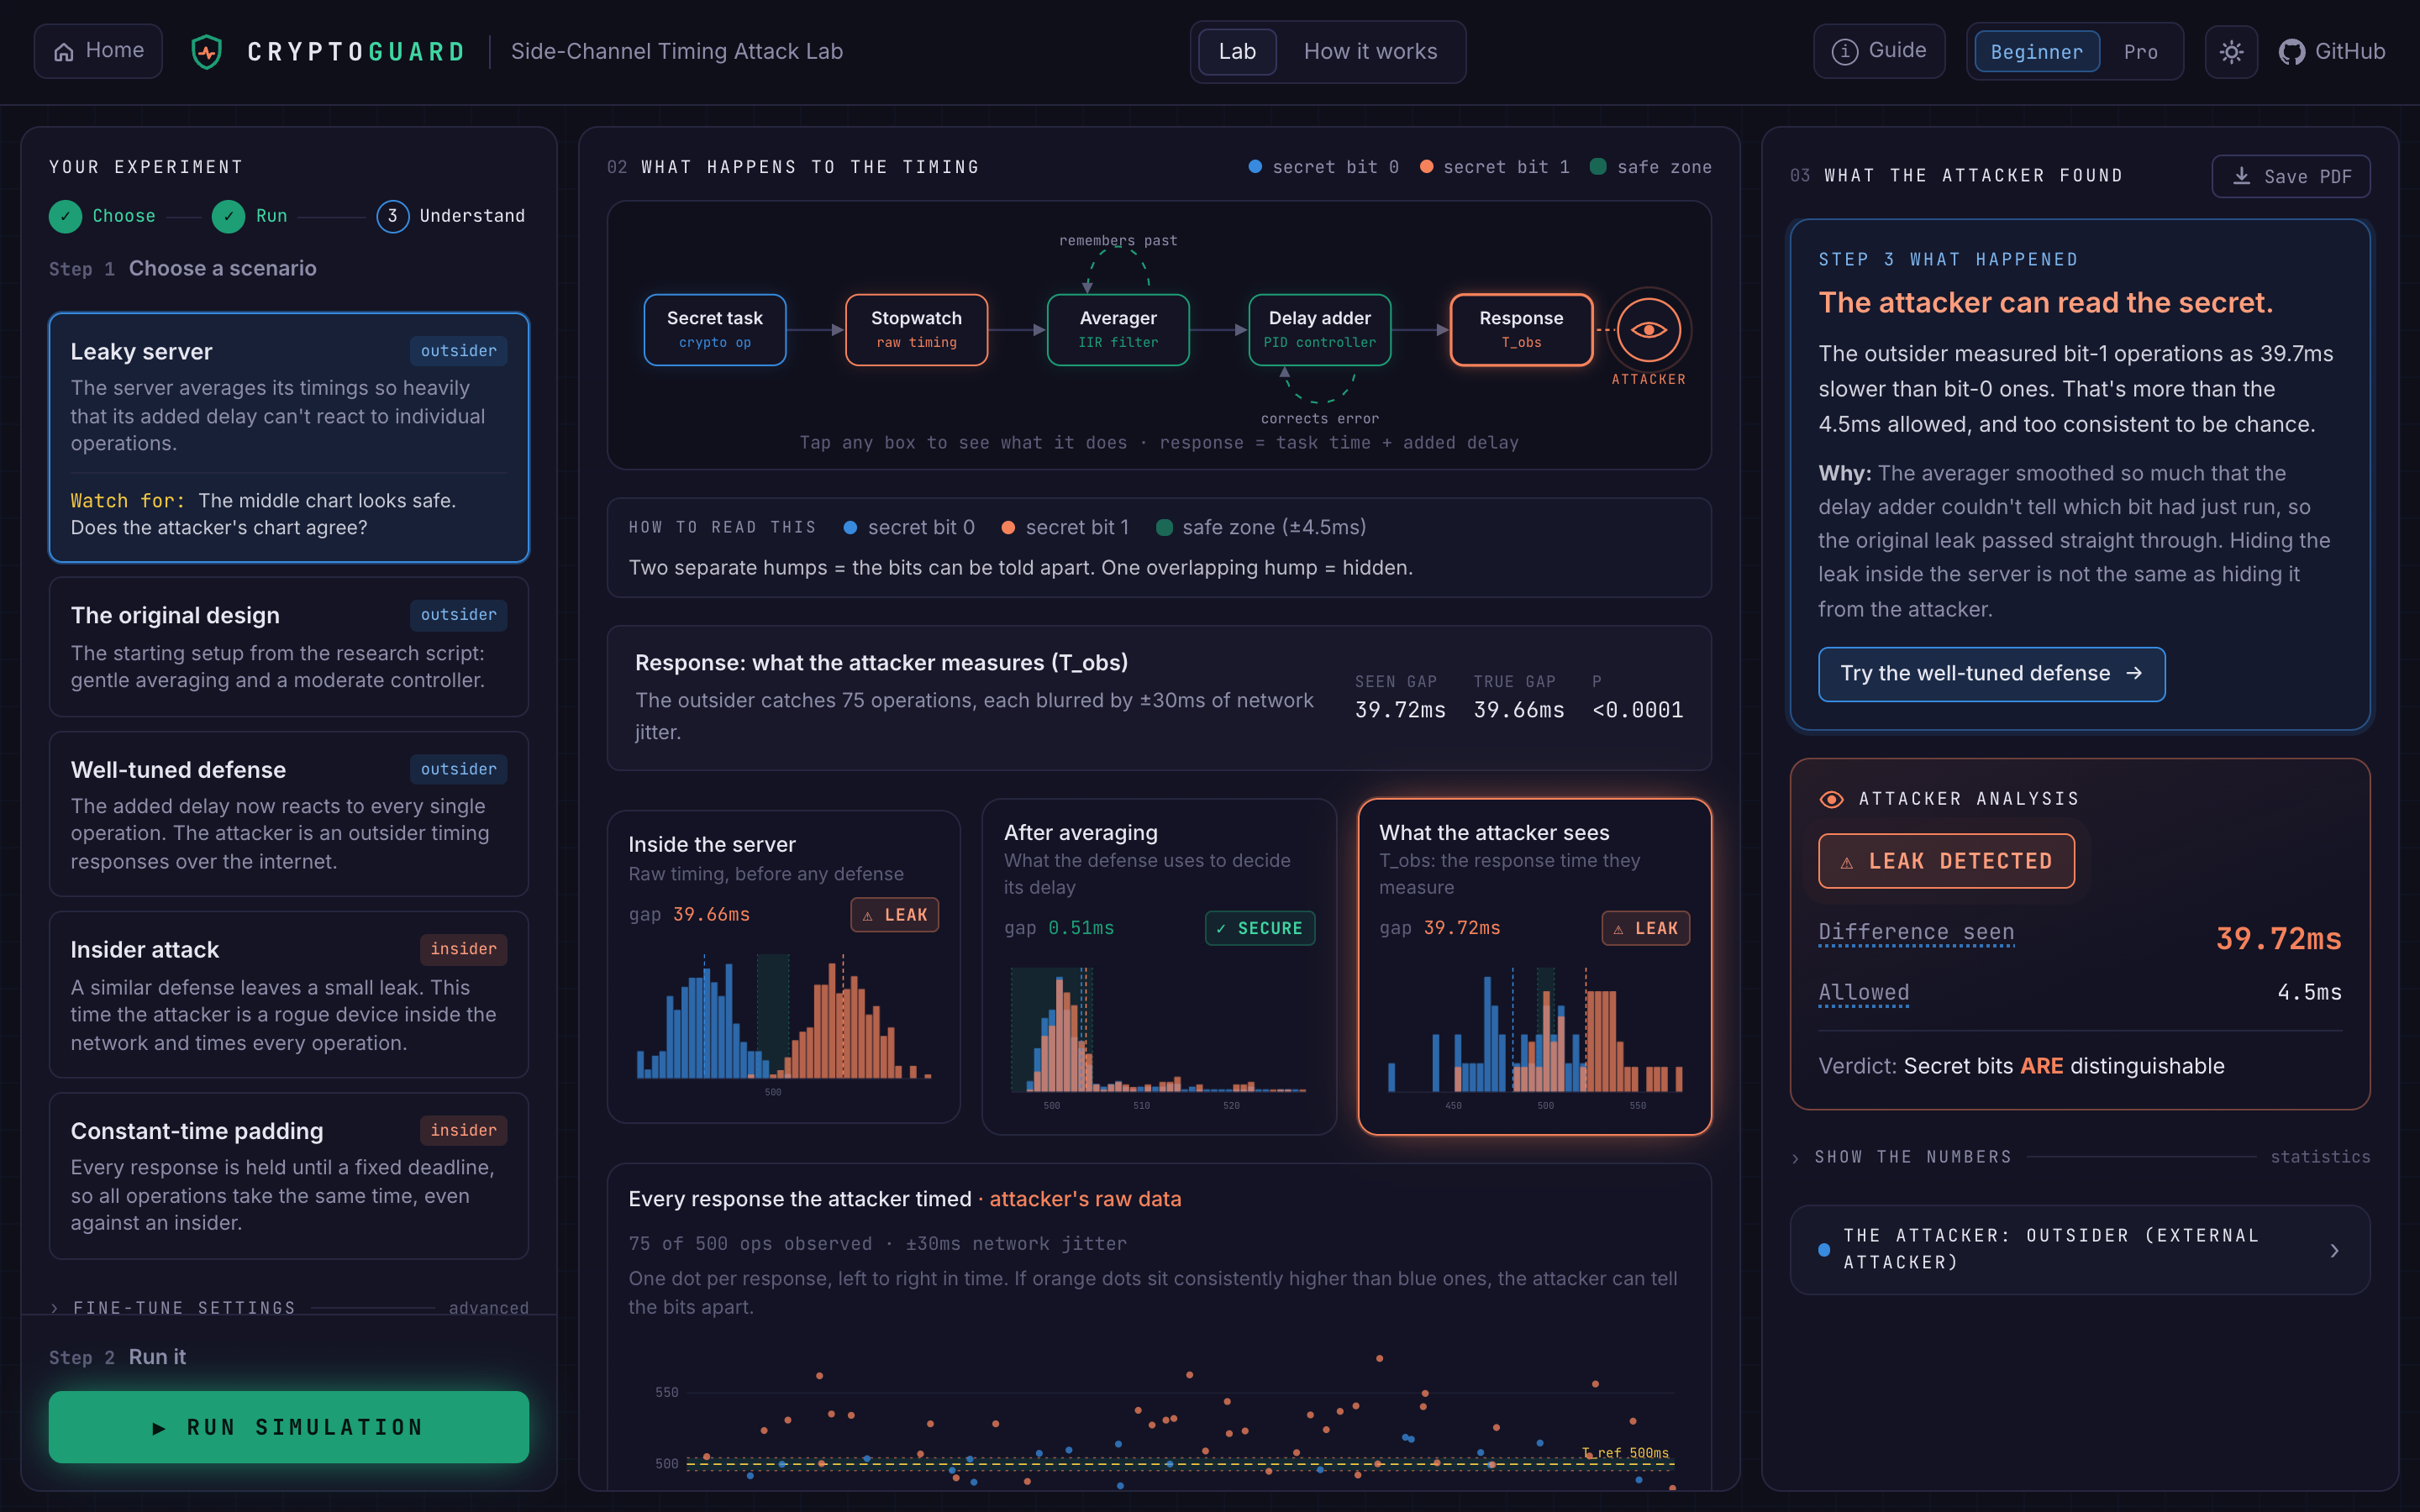
I built a guided simulation platform that models secret-dependent execution times, external and rogue-node threat models, network jitter, IIR filtering, PID-based delay control, Welch’s t-tests and WCET padding. Beginner mode explains each concept in plain language, while Pro mode exposes the complete technical configuration, pipeline visualisation and attacker statistics.
The outcome
CryptoGuard lets users reproduce timing leaks, compare defensive configurations and observe why smoothing can create a false sense of security. The experiments show that statistical tuning may reduce leakage, while constant-time WCET padding provides deterministic protection when its timing budget is not exceeded. Results can be exported as a PDF report.
React → TypeScript → Vite → FastAPI → Python → NumPy → SciPy → Matplotlib → Nginx → Docker → Traefik← Back to portfolio